Communications - Syslog
Communications equipment such as Cisco, Juniper or security enforcing devices such as Fortinet are integrated using syslog.
Most of device types in this category have little or no local buffering opportunities and as such Syslog/UDP is used.
While transmission to the default Syslog/UDP/514 HyperCollector port is supported, this is not recommended. Your source system should ideally not send data the default Syslog ports. Instead the following process is used:
- Create a custom syslog receipt port on the HyperCollector and assign a tag.
- Configure your local system to send the syslog data specific to a source to that port on those HyperCollector(s).
It is recommended to use syslog/UDP for communications equipment unless syslog/TCP with local spooling is directly supported, documented and the network device has sufficient capacity.
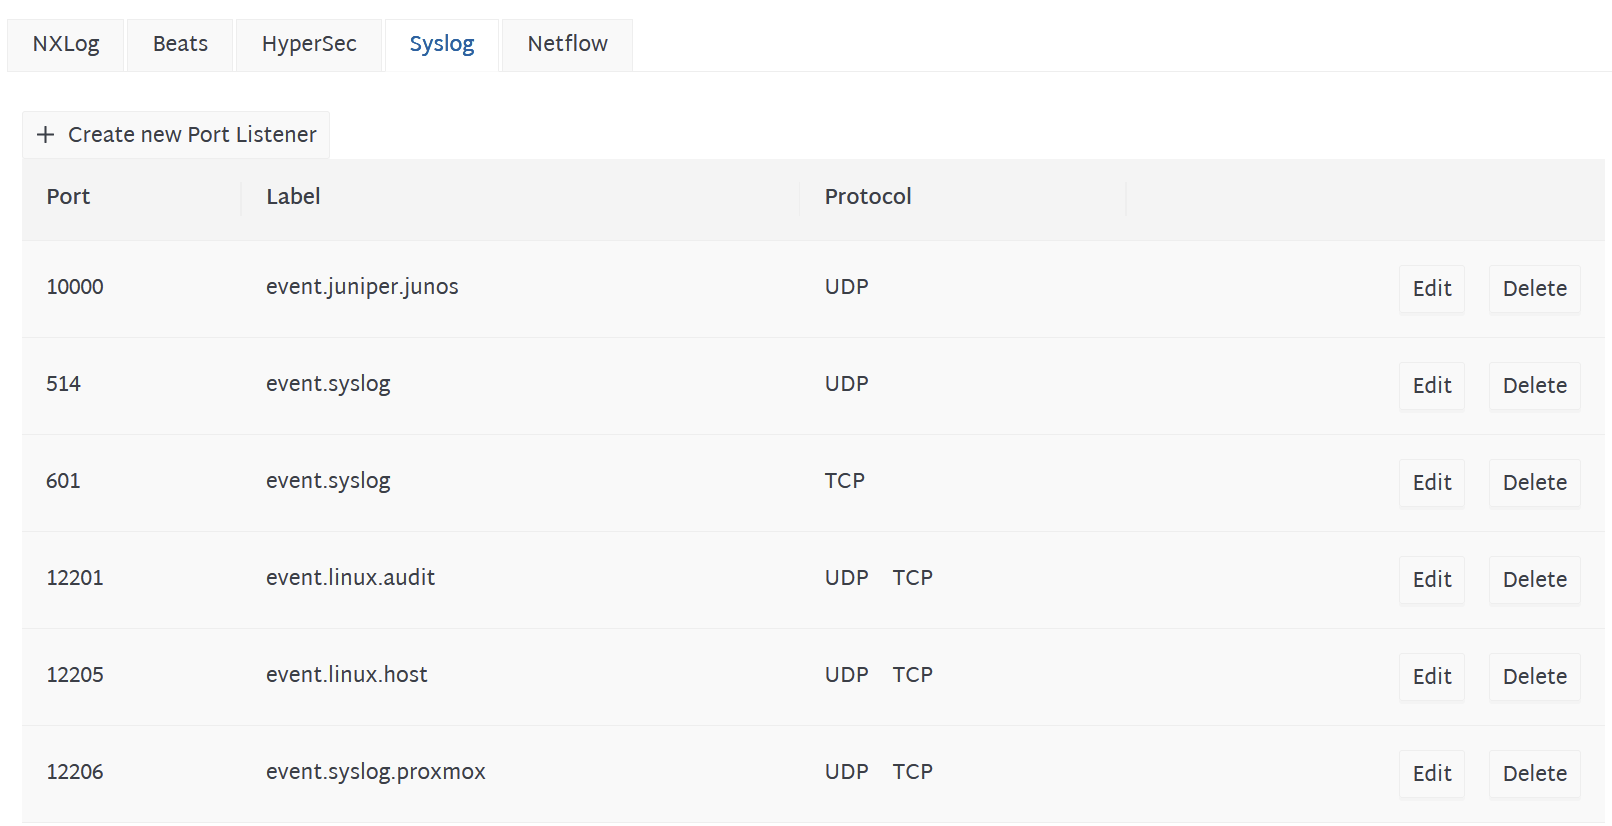
The example below adds Juniper Junos events UDP on port 10000. You would then configure your Juniper devices to send their syslog traffic to UDP port 1000 on the HyperCollector instead of UDP/514.